
Security & compliance
Security, information governance and clinical safety
Clear information for your governance review.
Review our approach to access, data handling and clinical safety, alongside the dated status of our assurance work. Your organisation’s assessment and approval remain part of each deployment.
Company assurance evidence last reviewed: July 2026. A later editorial review of NHS service rules does not update these assurance statuses.
Clinical safety
Clinical risk management: DCB0129 and DCB0160.
DCB0129 (manufacturer)
We are establishing DCB0129 clinical risk management as the software manufacturer: a named Clinical Safety Officer, a hazard log and a clinical safety case. This work is in progress.
DCB0160 (your deployment)
We support your organisation with its DCB0160 deployment clinical risk management; we do not claim it for you.
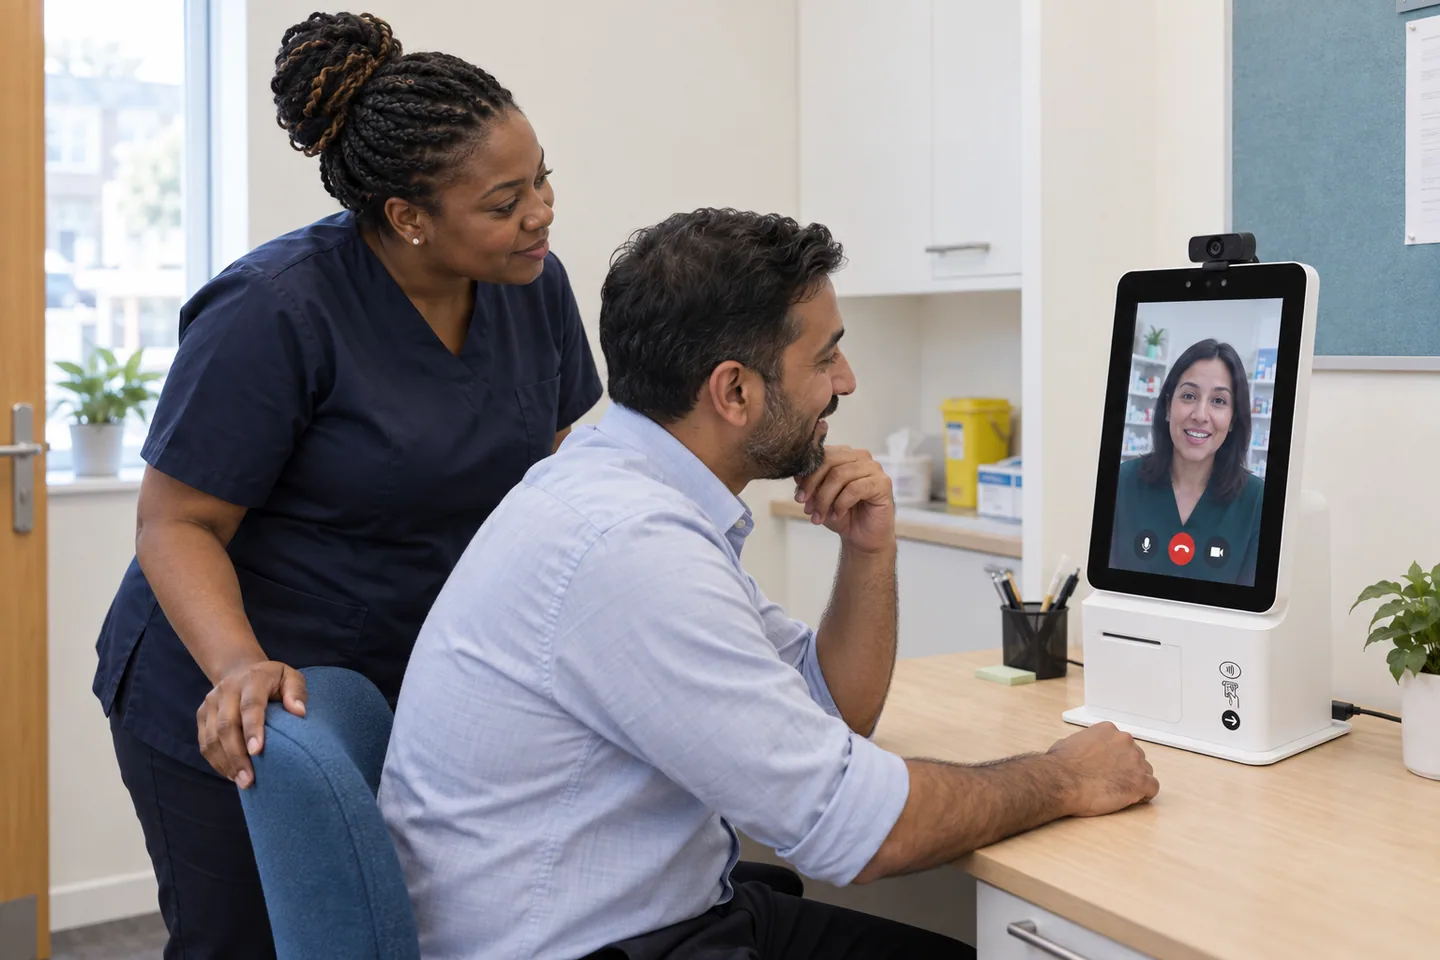
Your Responsible Pharmacist remains on the premises throughout. Remote Pharmacist adds consultation capacity by secure video; it never replaces your RP and never supervises dispensing remotely.
Data protection
Where your patients’ data lives, and how it’s handled.
UK GDPR and DPA
Designed for UK GDPR and the Data Protection Act, with controller vs processor set out per service mode. ICO registration is in progress.
Data minimisation
Review the information collected, access permissions and retention requirements for your service. Website analytics excludes enquiry contents and clinical-app activity.
UK residency and encryption
Built for UK data residency: records and any recordings held in the UK, encrypted in transit and at rest.
What your IG lead receives
The pack we walk through with you
- Data-flow map for each service mode
- DPIA support for your assessment
- Draft data-processing terms (labelled as drafts)
- Controller / processor responsibility matrix
- Pathway-by-pathway remote-suitability matrix
- Convert-to-face-to-face protocol
- Sub-processor and hosting list
- Retention and deletion schedule
Access and privacy
How access is controlled
- Individual accounts and multi-factor authentication support
- Role-based permissions for clinical and administrative work
- Website analytics separate from the clinical app
- Recording off by default, consent-gated when used
Recording, when a service uses it at all, is consent-gated, visibly indicated, signed-URL access only and retention-controlled.
Access and audit
Access controls and a traceable record.
An append-only, hash-chained audit trail records clinical and administrative activity. Review the audit scope, recorded events and access permissions as part of your deployment assessment.
Our clinicians
Consultations are delivered by GPhC-registered, appropriately indemnified pharmacists, aligned to the GPhC February 2025 guidance for services provided at a distance.
Safe prescribing
A documented convert-to-face-to-face protocol and a pathway-by-pathway remote-suitability matrix.
See how this works in practice: how a consultation works, the NHS Pharmacy First service, and the services you can deliver. For website data, see our privacy notice.
Security FAQ
What IG leads ask us first.
Where is patient data stored?
The platform is designed for UK data residency, with encryption in transit and at rest. Review the hosting, recording storage, backup locations, access permissions and retention arrangements for your deployment in the information-governance assessment.
Is the platform NHS DSPT compliant?
Our NHS Data Security and Protection Toolkit assessment is in progress. The footer lists assurance topics; their current status is set out on this page. Listing an assurance topic is not a claim of certification. Ask us for the current evidence.
Who is responsible for clinical safety?
We are establishing DCB0129 clinical risk management as the software manufacturer, with a named Clinical Safety Officer, a hazard log and a clinical safety case in progress. Your organisation runs DCB0160 for its deployment, and we support that work rather than claim it for you.
Is video recording always on?
No. Recording is off by default, policy-driven and consent-gated. When it is used, access is by signed URL only and retention is controlled per policy.
Can we see the audit trail?
Yes. An append-only, hash-chained audit trail records clinical and administrative activity. We can walk you through the recorded events, access permissions and audit scope for your proposed service.
Talk to us about your IG sign-off
We’ll walk your superintendent or IG lead through the detail and share our documentation.